

Quality
DevelopmentProd
Risk posture
PermissiveRestrictive
Your pipeline, your policies. Enforced at the speed of AI
Ship faster and mitigate risk.
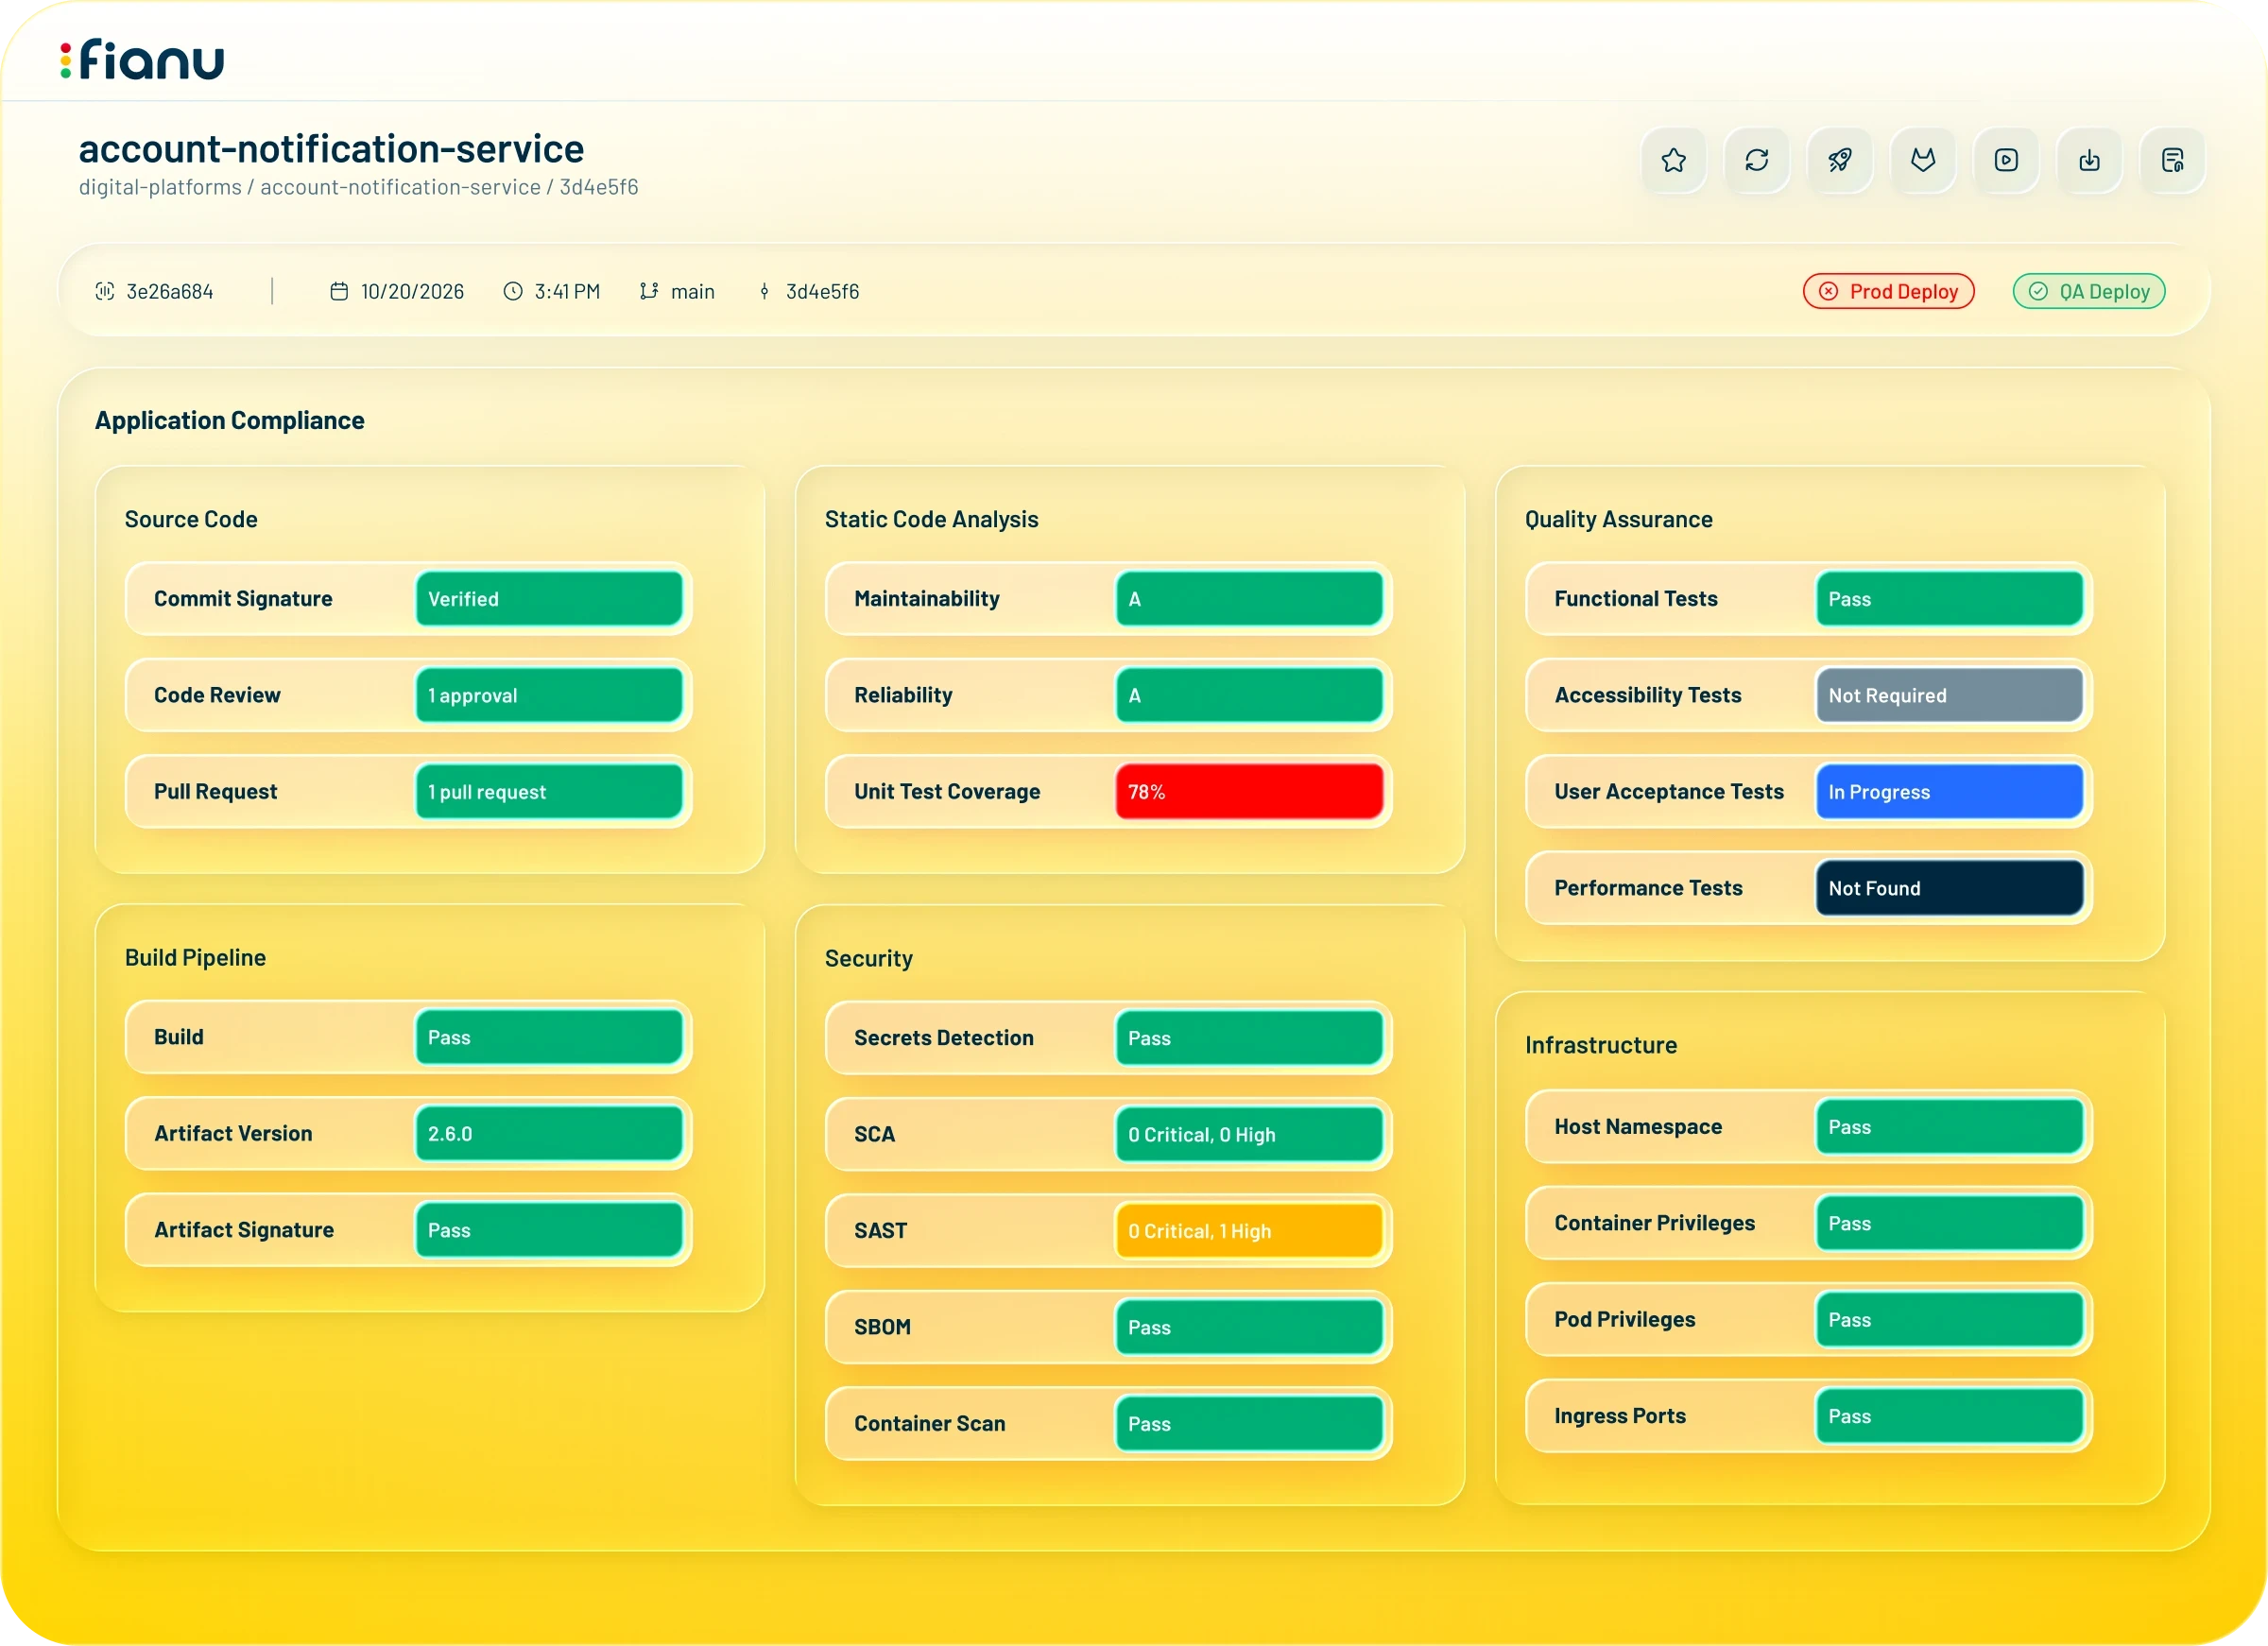
The average Fianu customer generates over 16 terabytes of evidence every year.
Per customer, per year
20m
Attestations
captured
2.6m
Artifacts
gated
1.4m
Commits
tracked
A governance layer across every path to production, with no pipeline changes. Enforce almost any requirement in minutes.
Fianu collects evidence from 60+ integrations and the API as it's produced, so controls evaluate real tool output, not screenshots or manual reports.
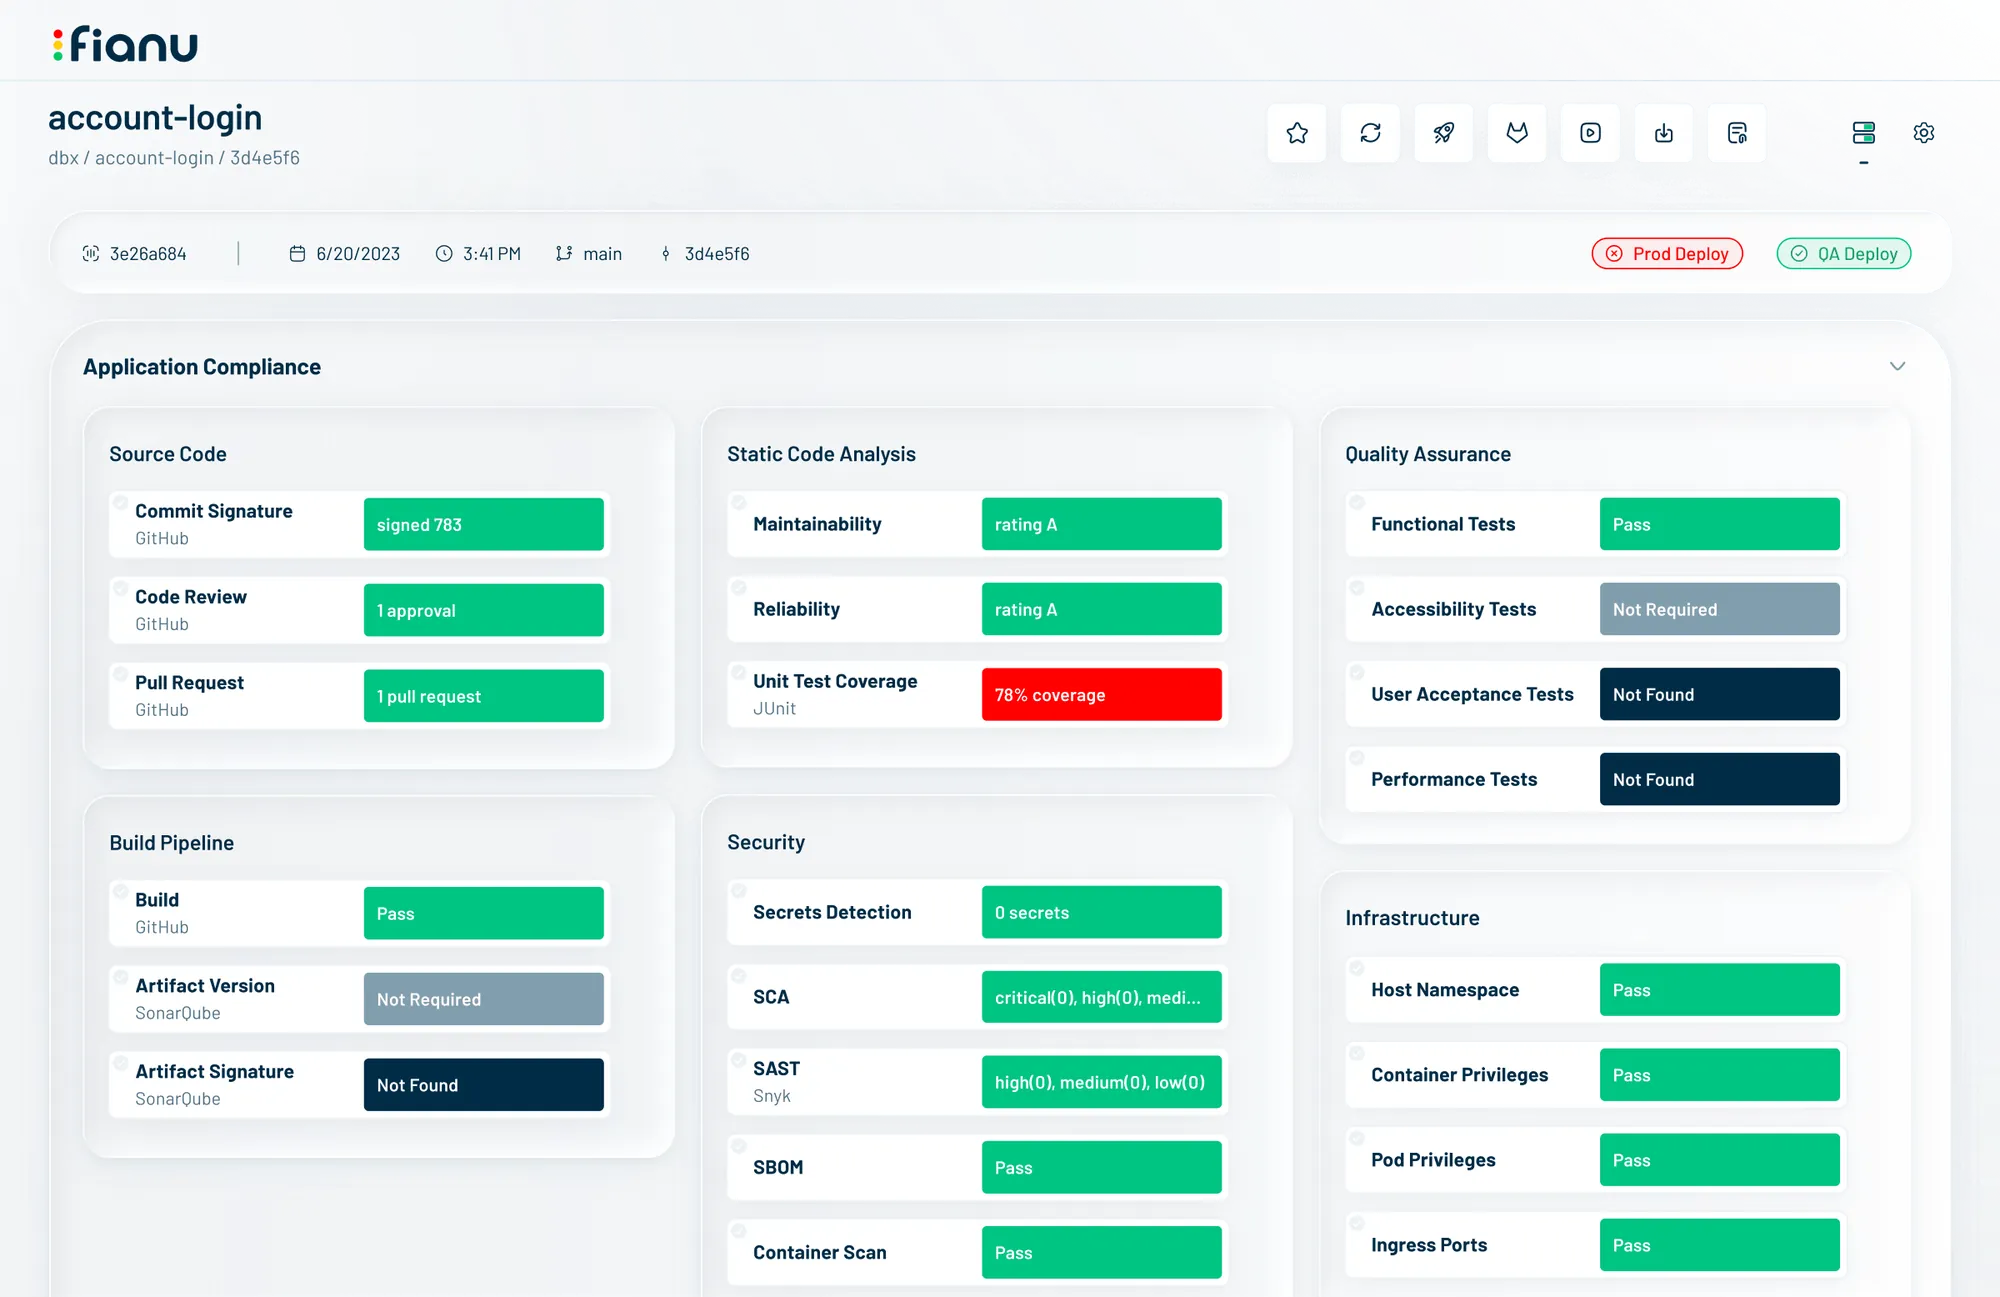
Every control evaluation produces an immutable, signed attestation of the evidence, policy, and result, proving compliance per artifact, repository, or release.
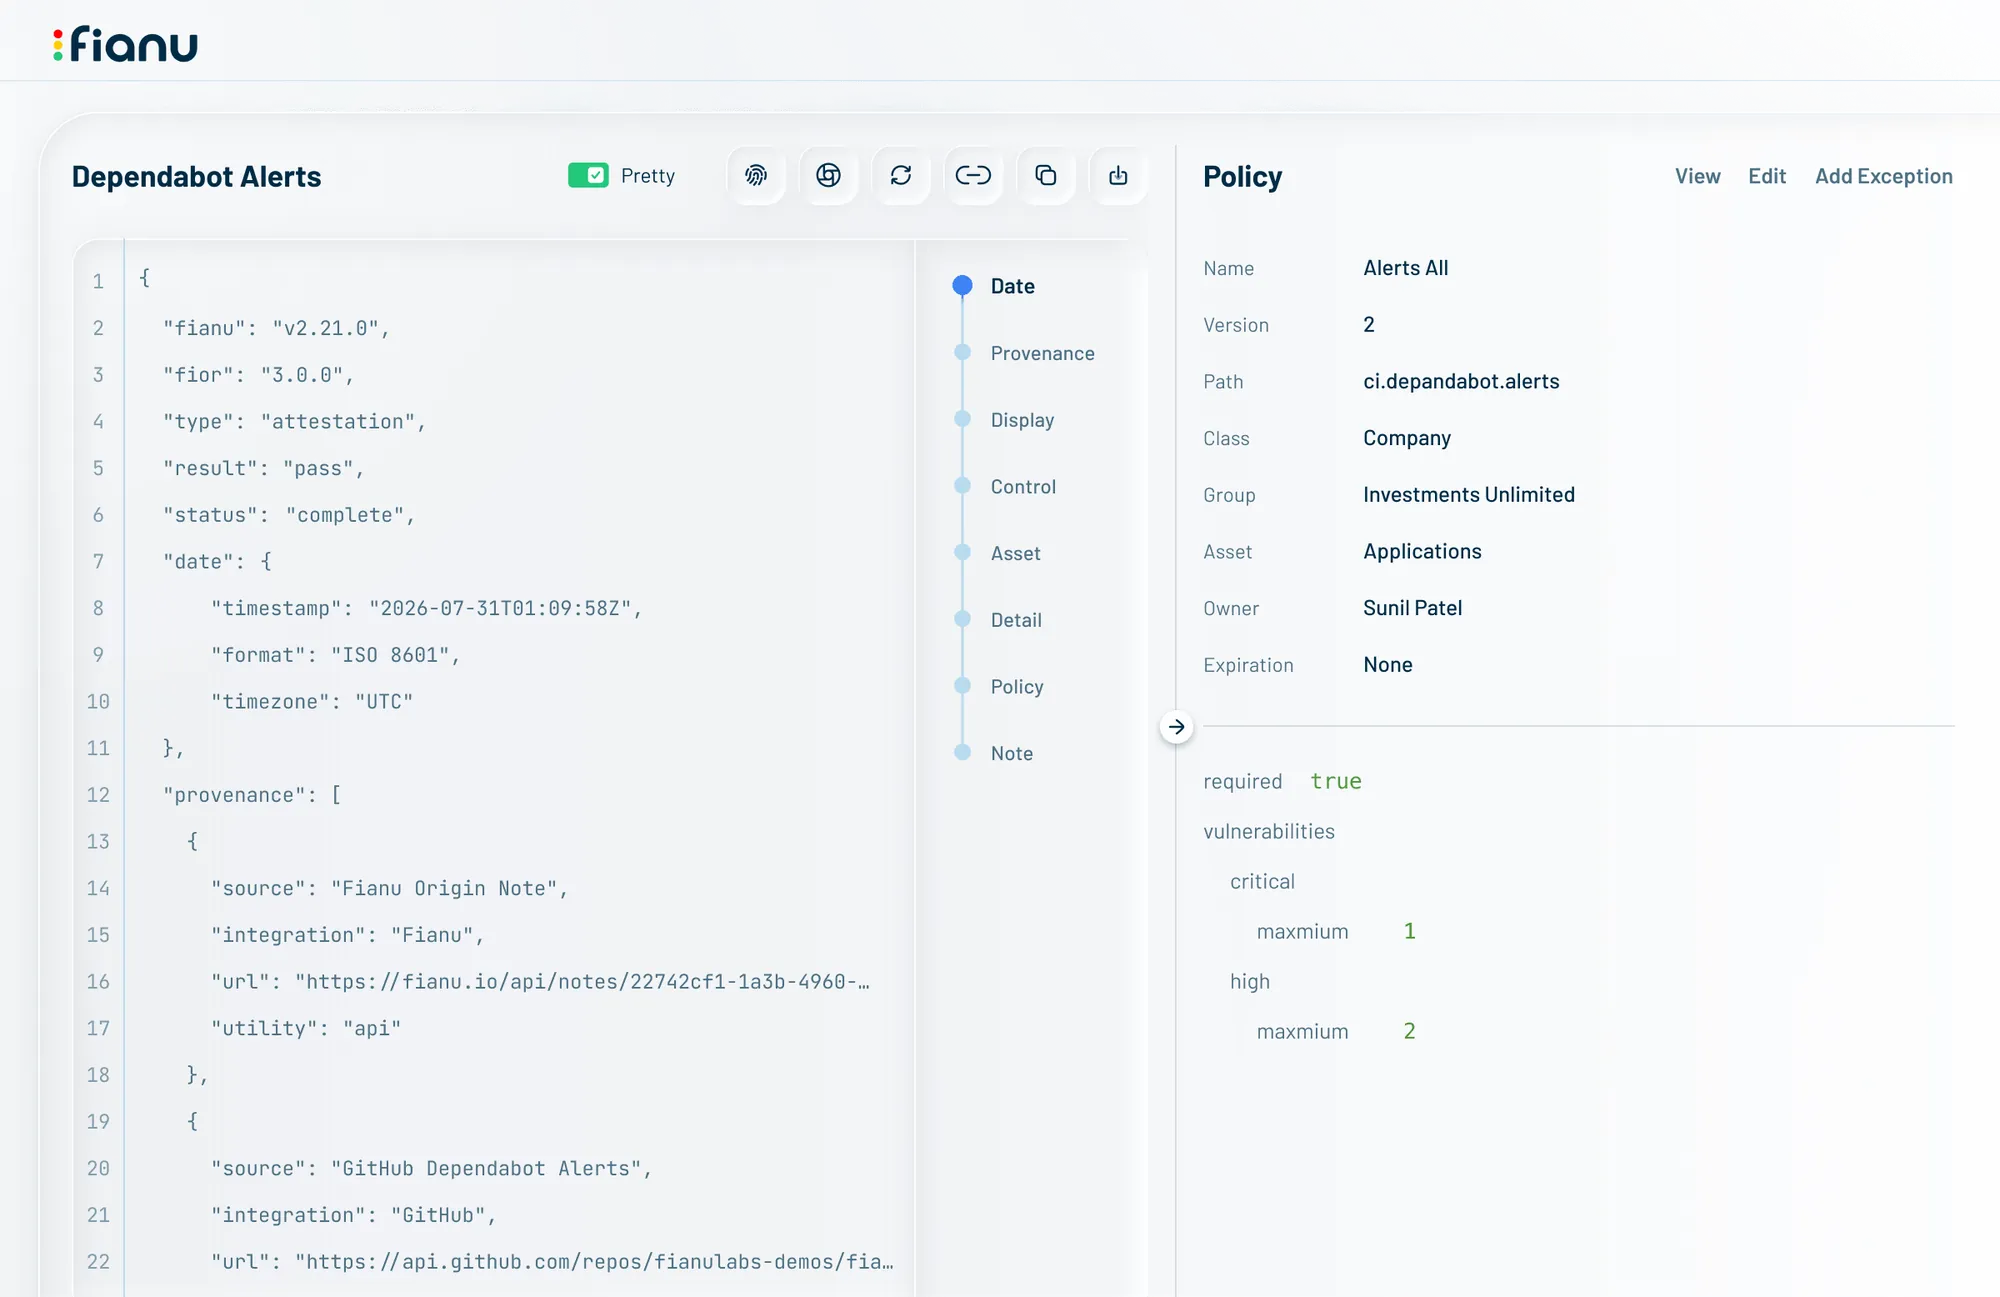
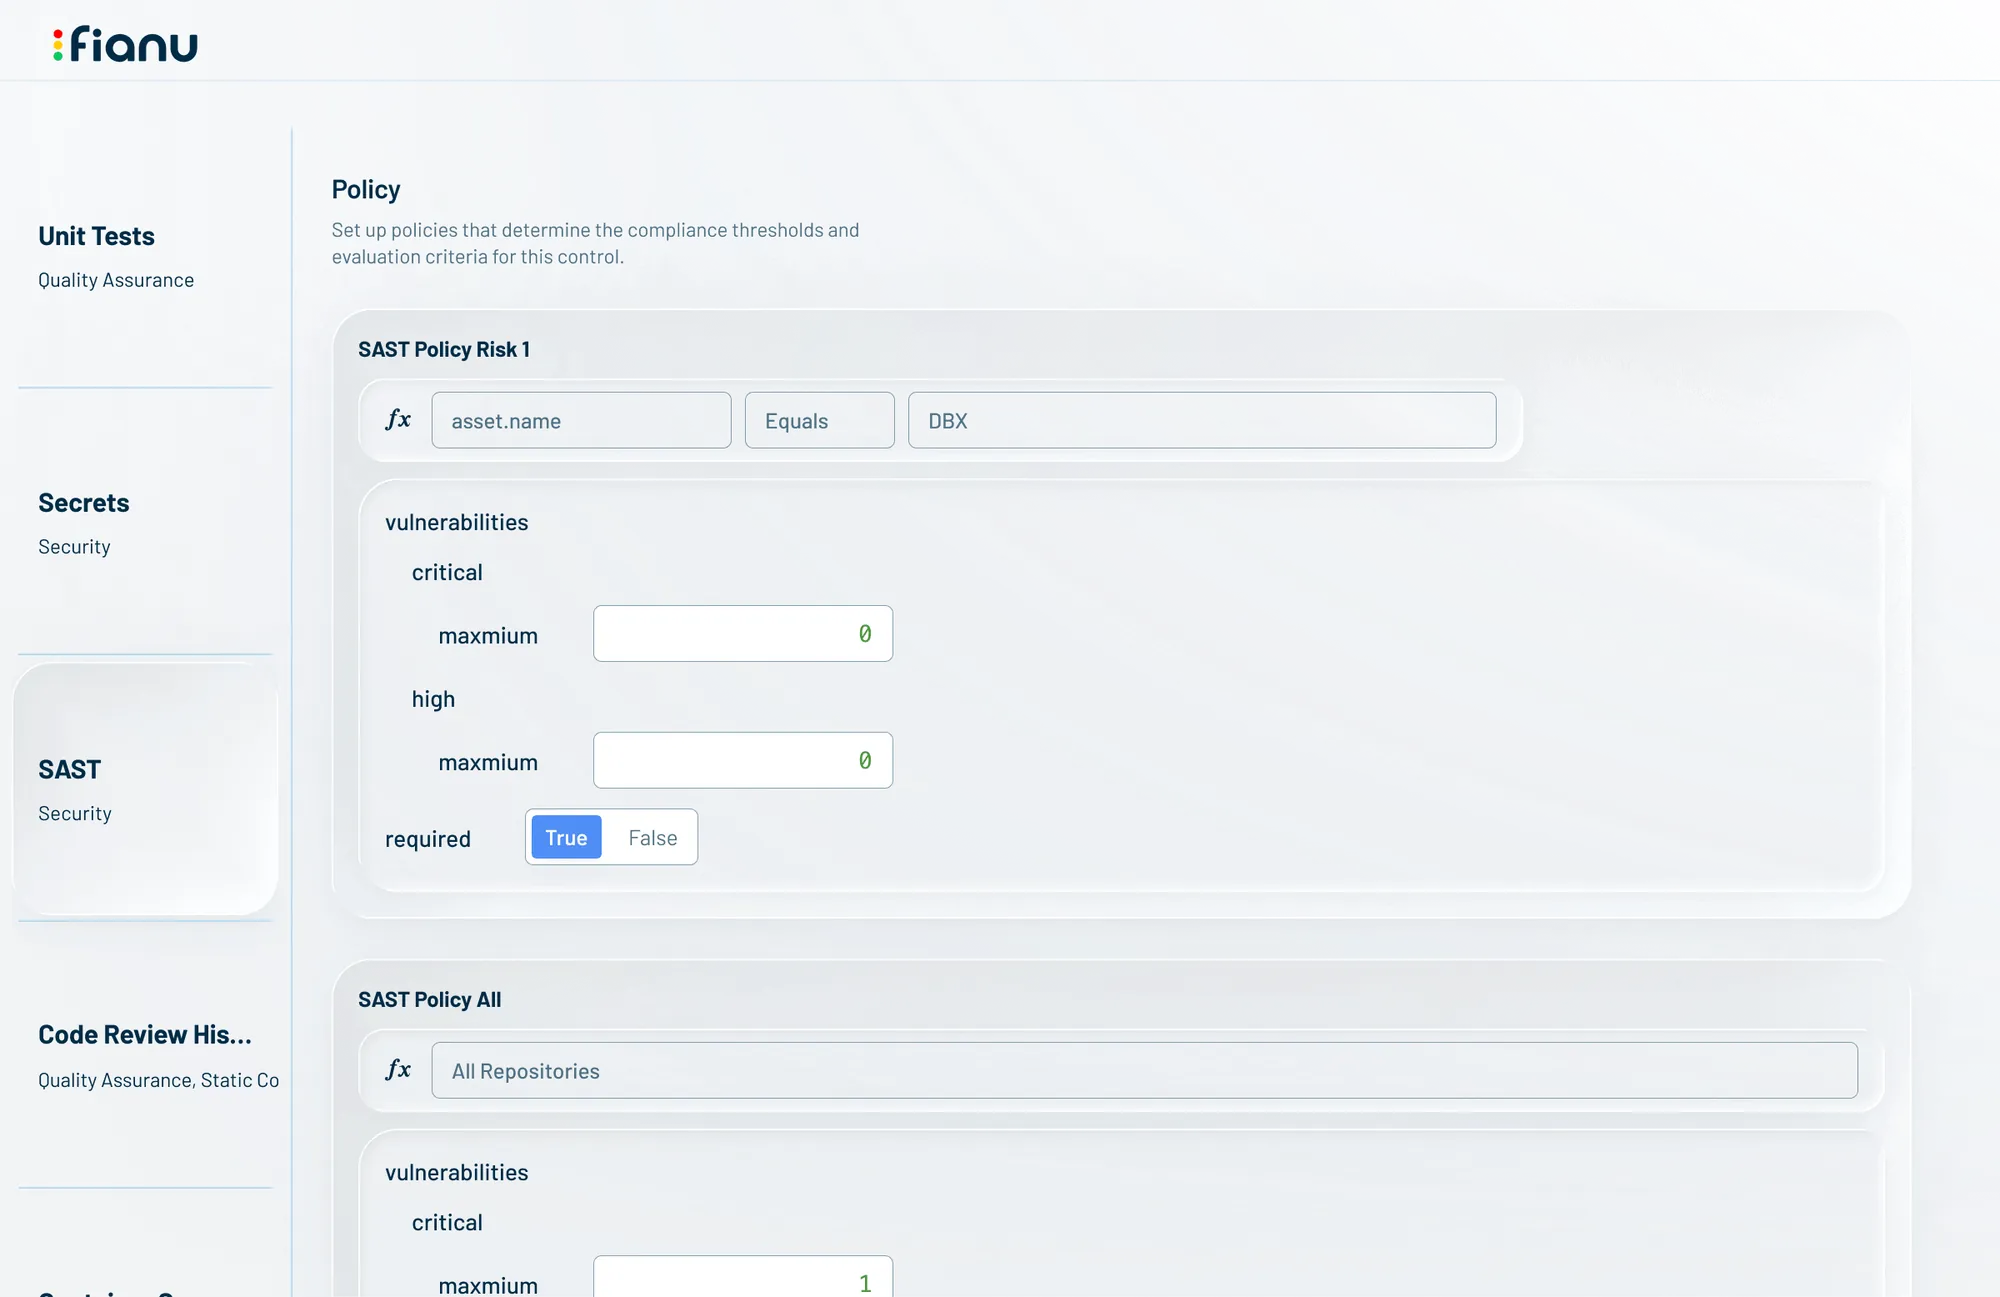
Policies set control thresholds and layer along your asset hierarchy, from an enterprise baseline down to a single repository. Every change is versioned and access controlled.
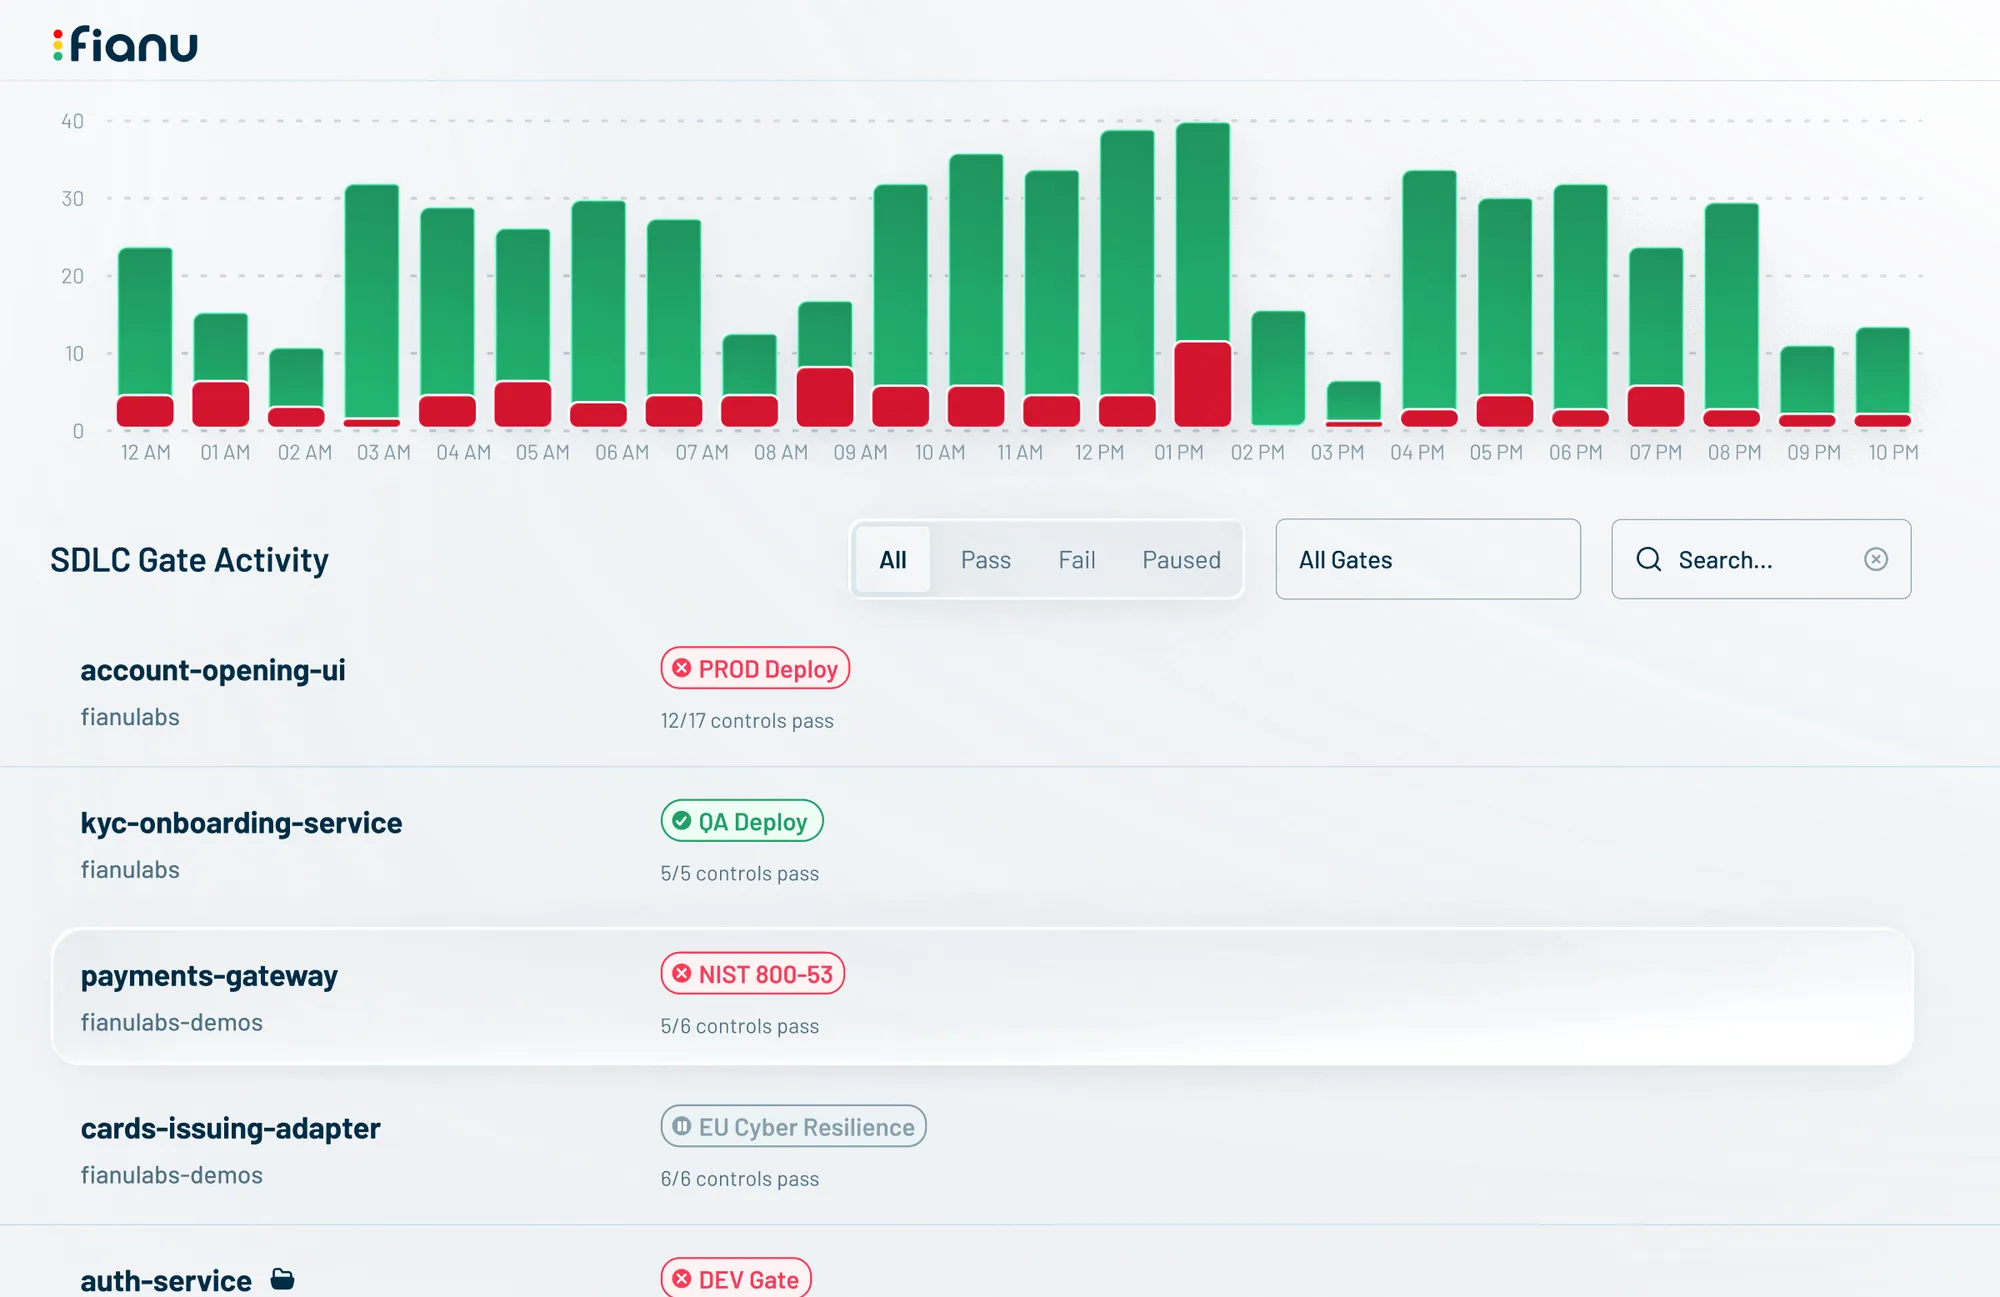
Gates enforce control results from pull request to build to deployment, blocking an artifact or a whole release. Native integrations, API, CLI, or MCP, with no pipeline code changes.
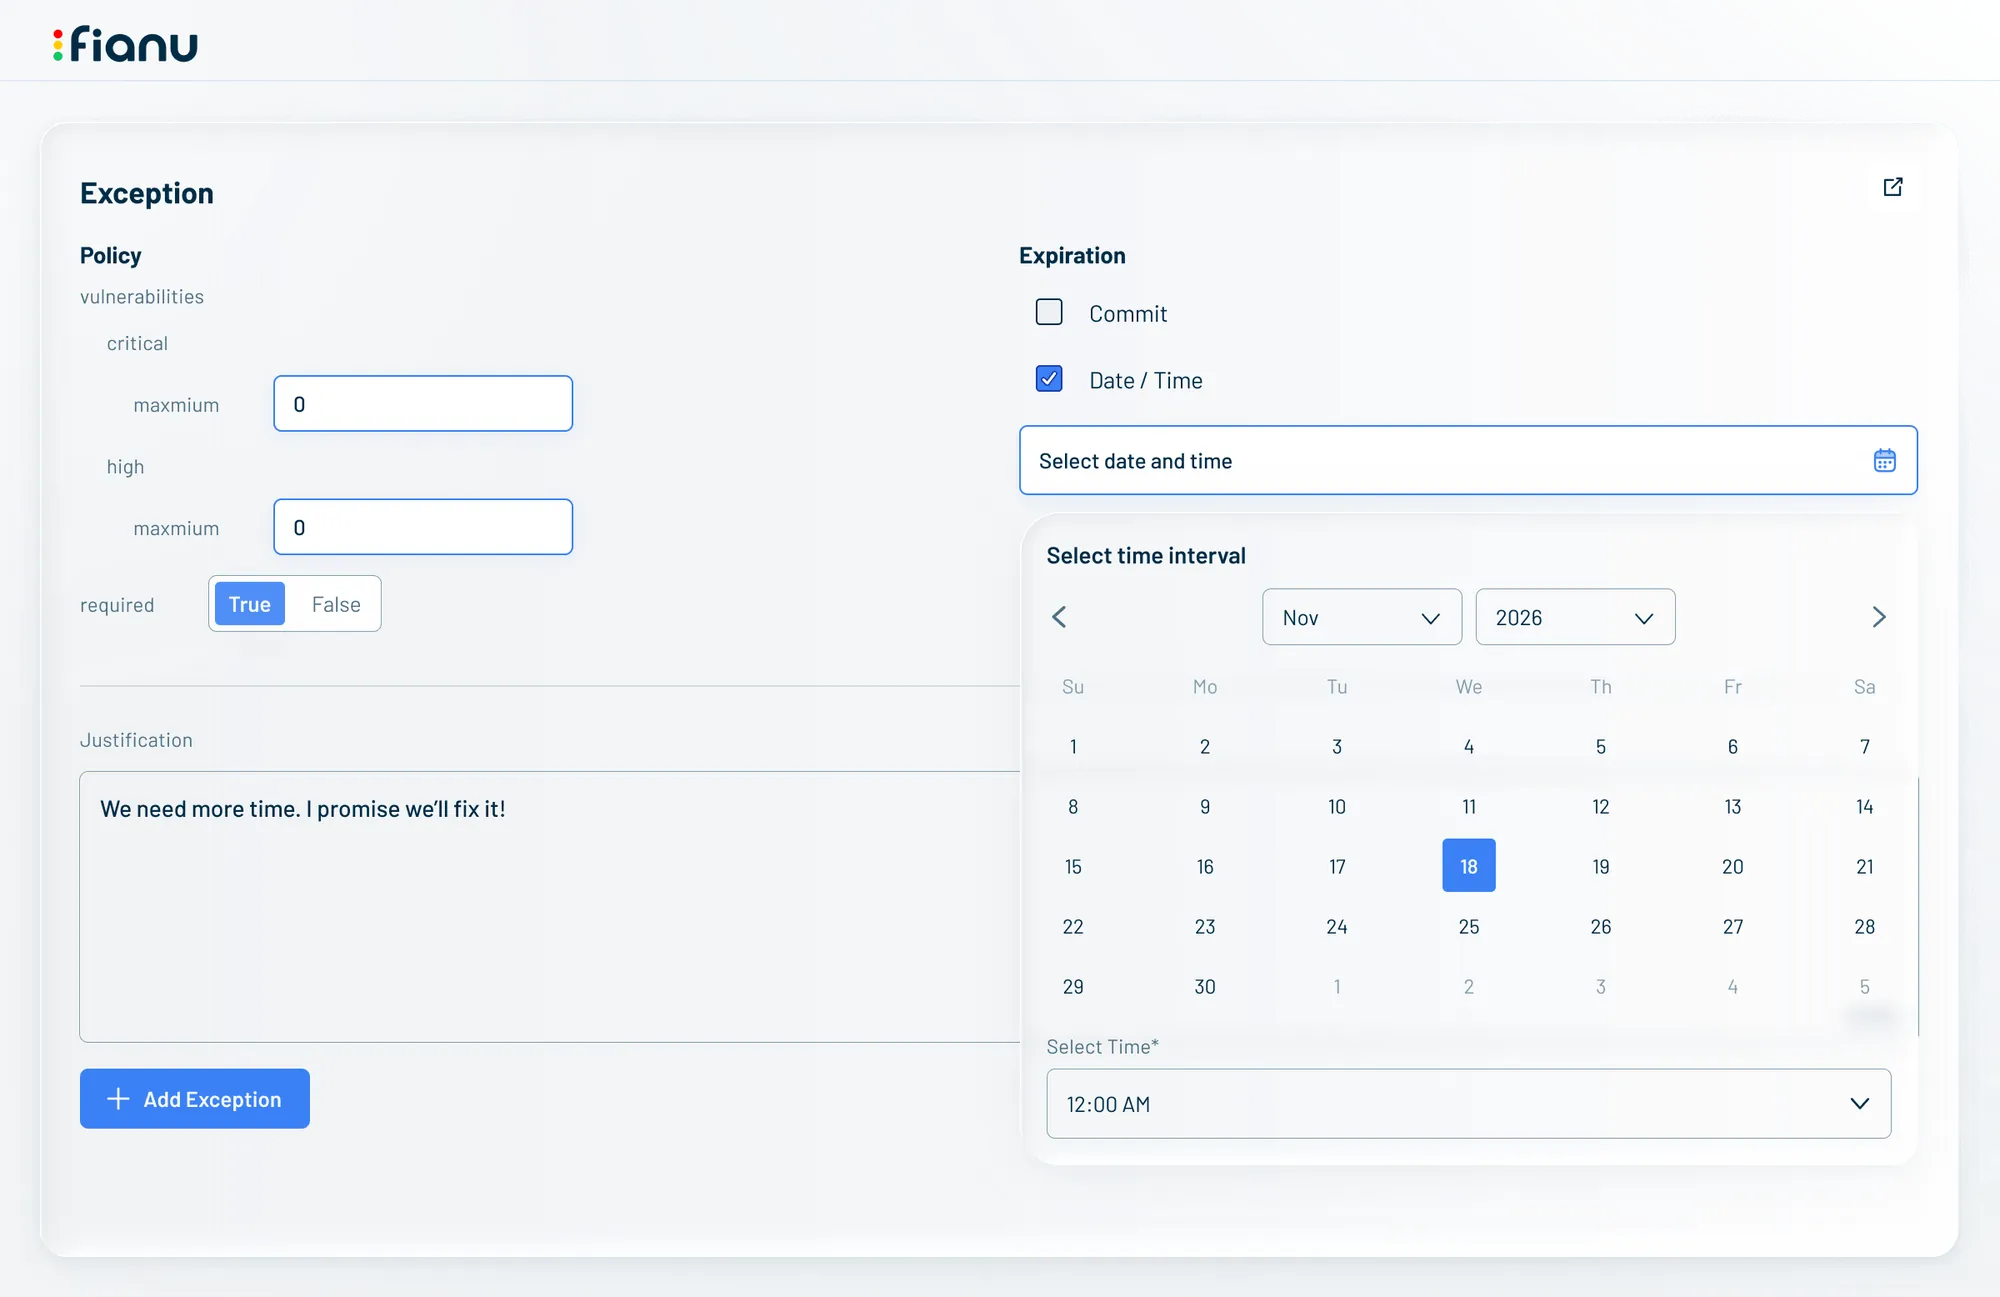
Time-bound exceptions ease or waive a requirement for specific assets, approved by policy owners and kept in the record, so auditors see what was excepted, by whom, and for how long.
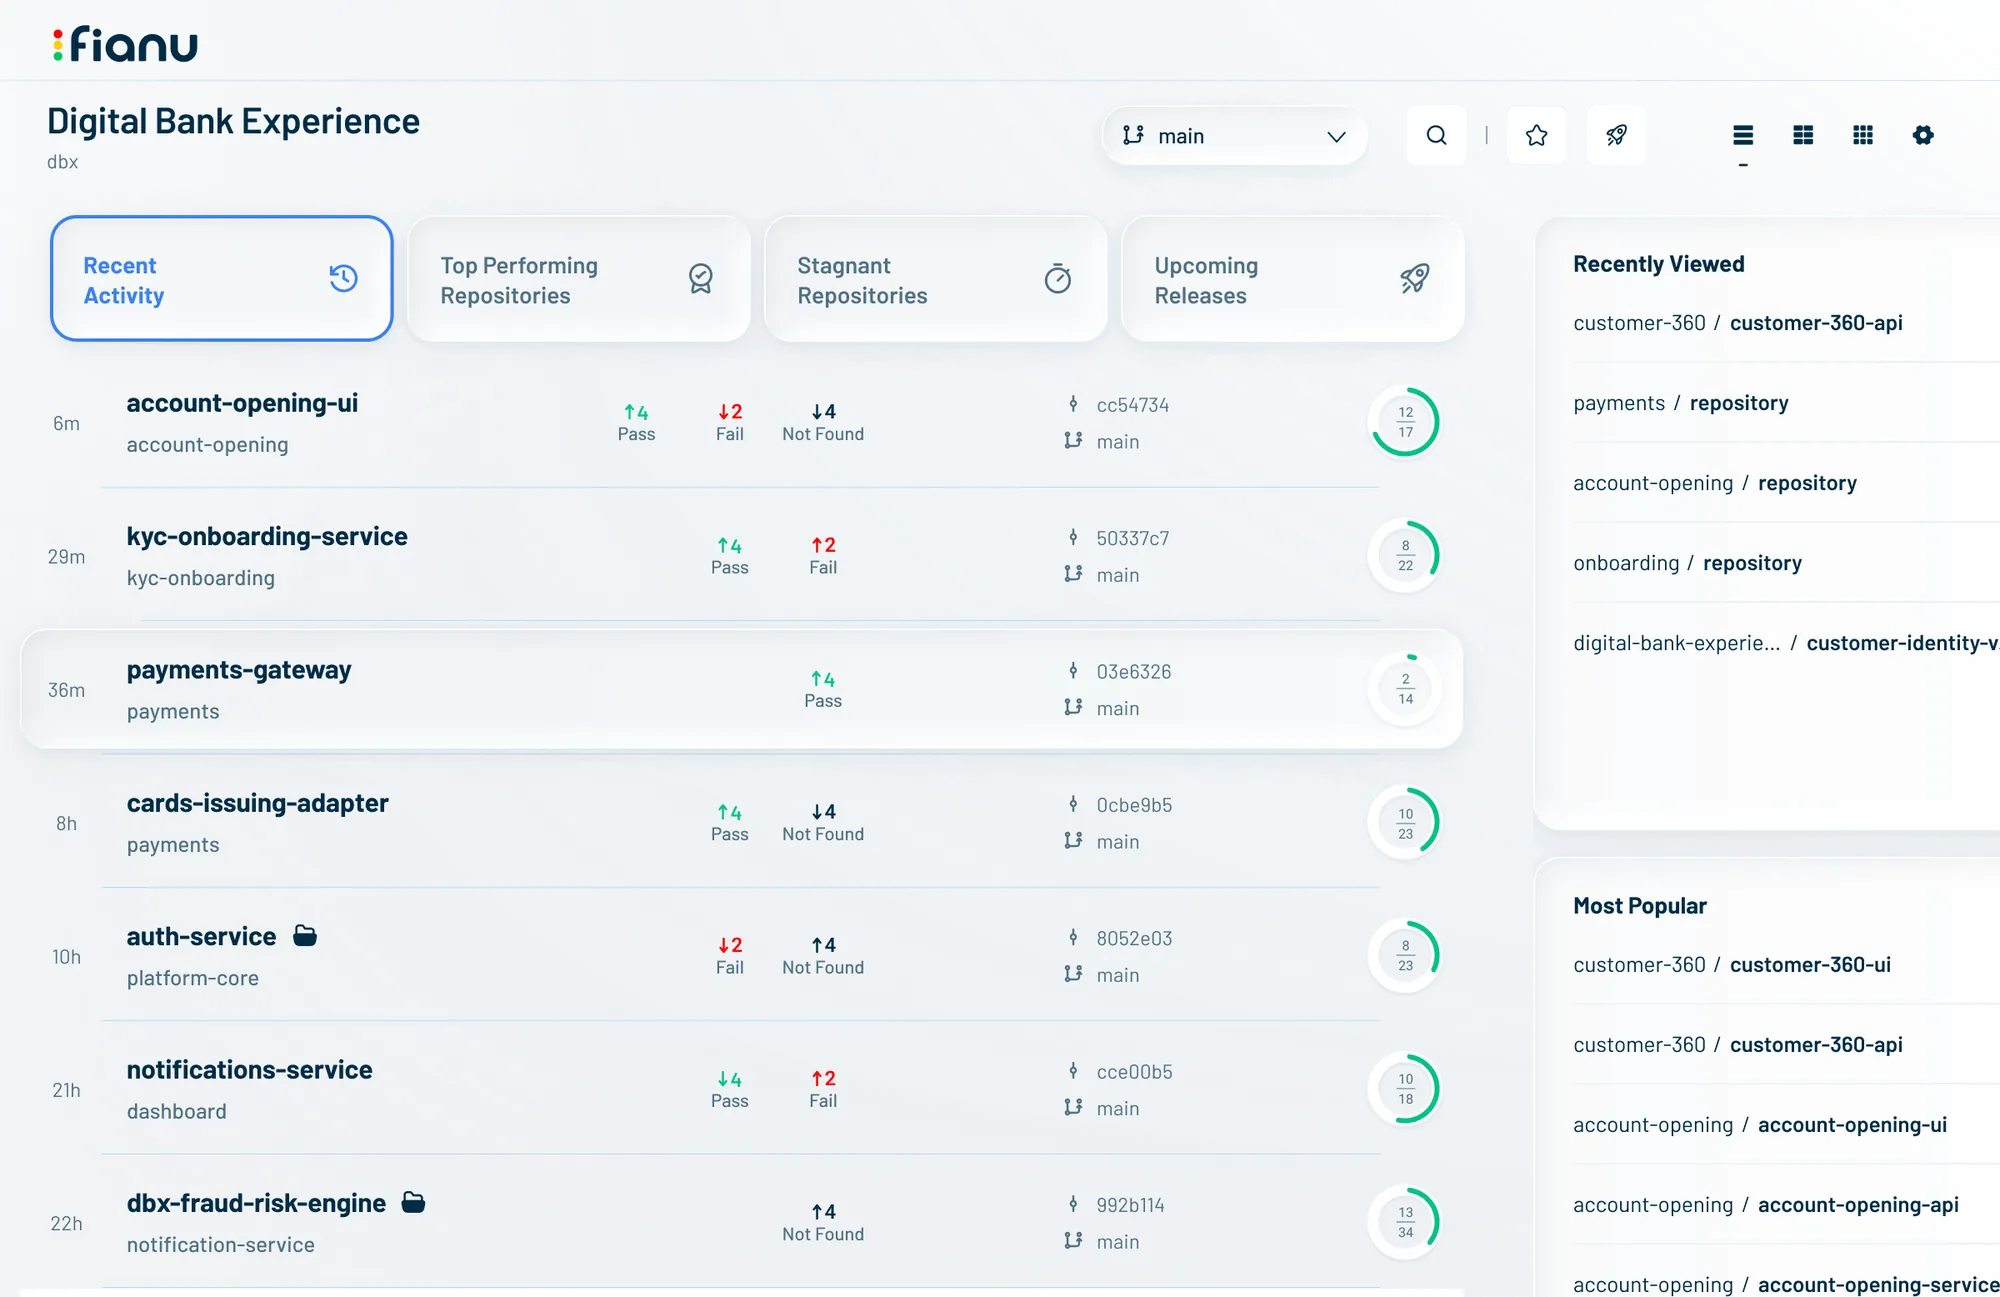
A live inventory of repositories, modules, and artifacts, organized under your business hierarchy, with ownership and compliance posture rolling up at every level.
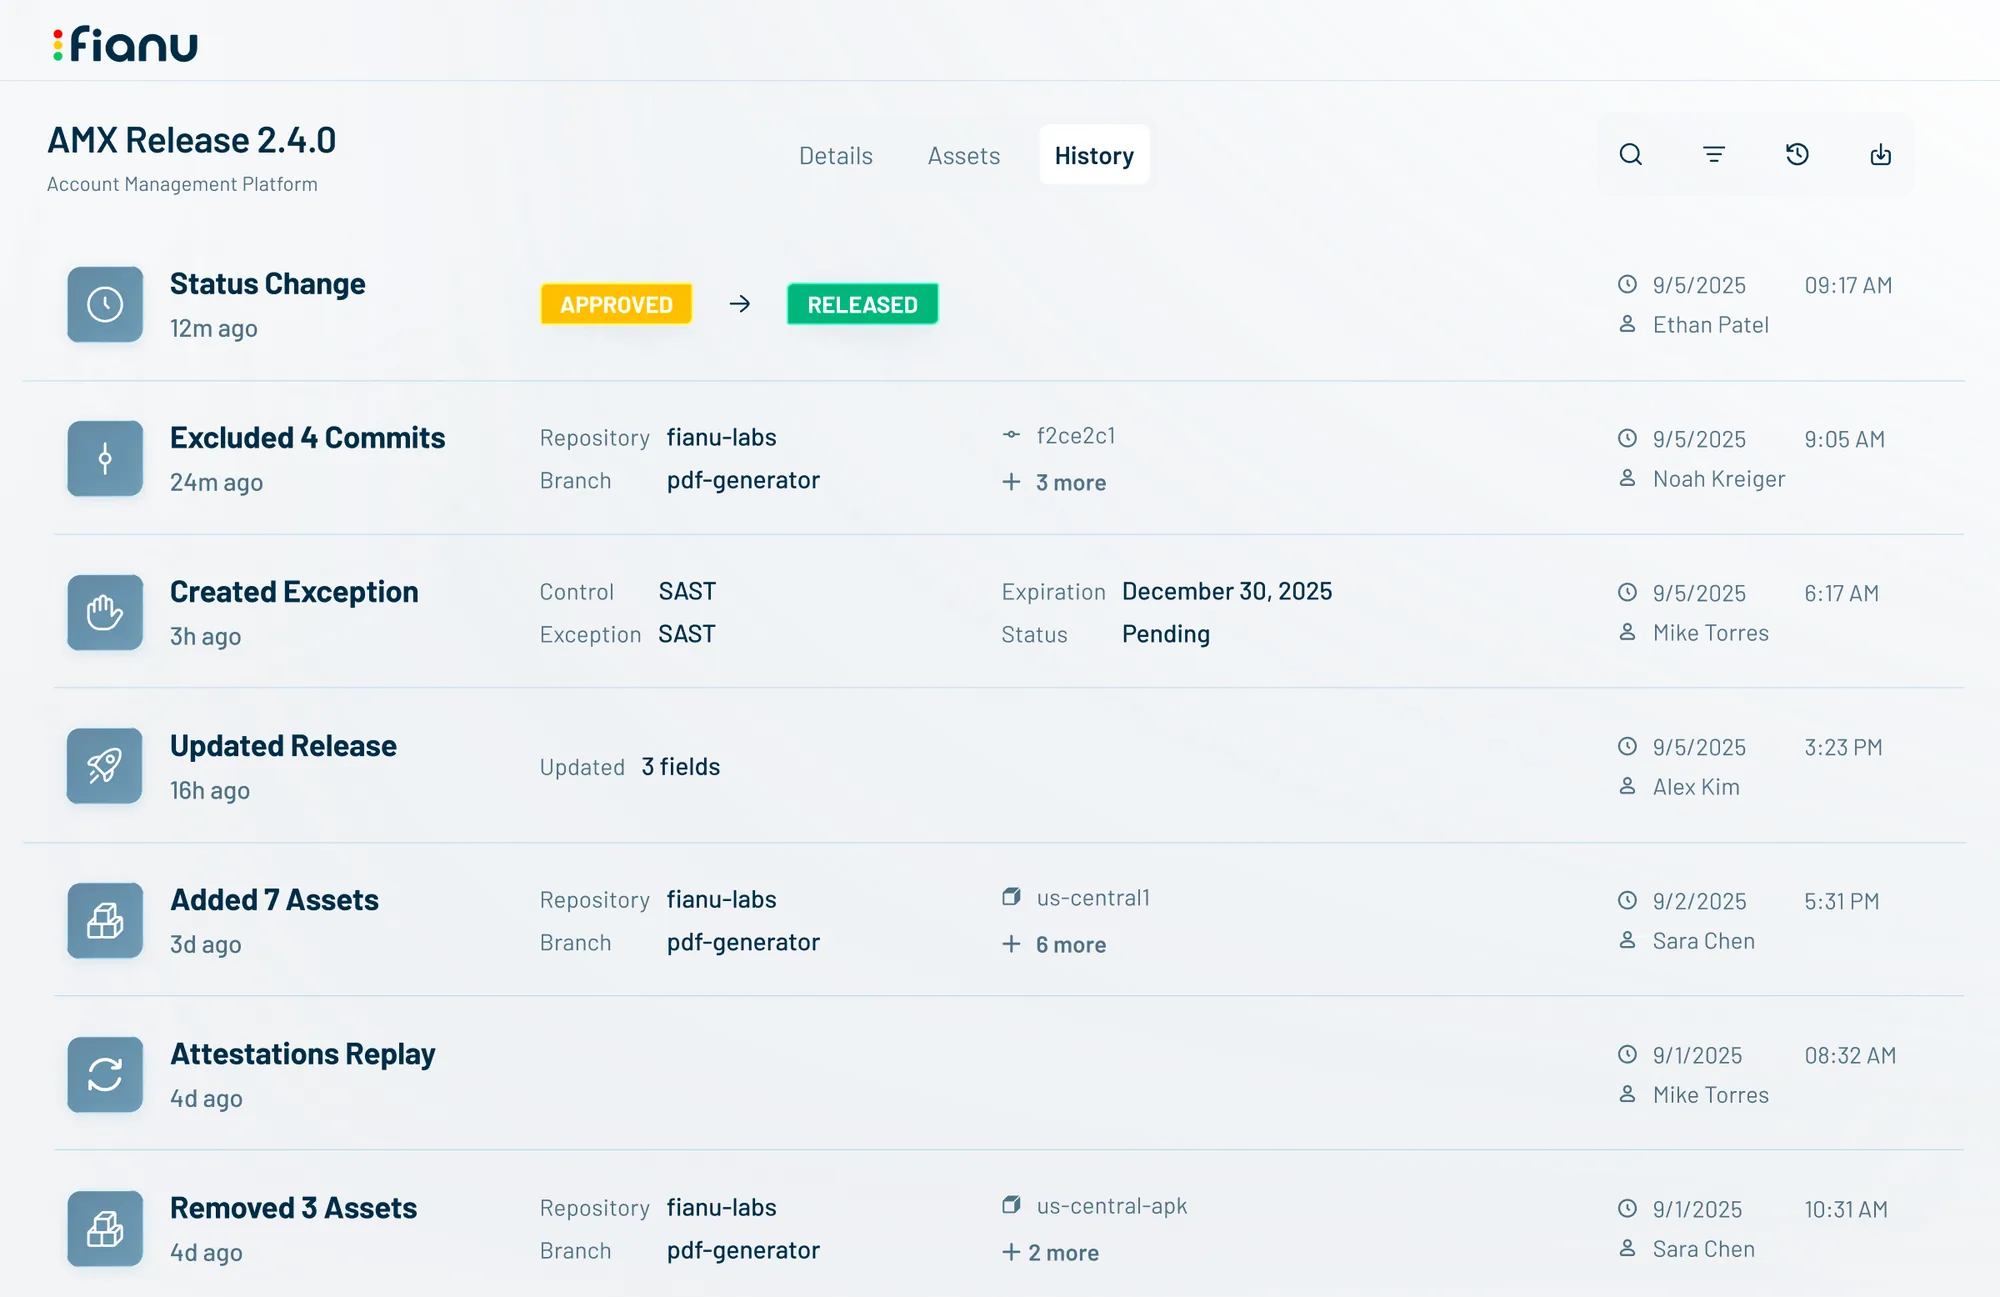
Every attestation, policy change, exception, and gate decision is kept in a tamper-evident record. Closed releases lock in place, so auditors can reconstruct exactly what shipped.
55+
 Controls
Rulesets for evaluating evidence against policy.
100+
 Policies
Requirements for measuring and enforcing compliance.
65+
 Integrations
Third-party integrations for capturing evidence.
With over 40 toolchain plugins across CI/CD, security, quality, and change management, Fianu starts generating attestations on day one. No pipeline rewrites, no new workflows for your developers. And if you need something bespoke, custom plugins are a first-class citizen.
View our documentationFianu eliminates weeks of toil from our release process. In less than one year we reduced our release cycle times by 85%.
Facing rapid growth and mounting federal regulation, Dexcom needed security and quality compliance without giving up velocity. With Fianu enforcing policy gates and automating FDA evidence documentation across their DevSecOps pipeline, they now ship with speed and safety at the same time.

$45b
Market Cap

Regulator
85%
Faster time to market after using Fianu for twelve months
40 hours
Manual compliance work eliminated on every software release
Everything else lives in the docs: architecture, plugin SDK, policy language reference, and so on.
Read the docsAny signal from your toolchain: a scan result, a passing build, an approved ticket, a deployment. Automated watchers record each as a time-stamped, immutable event, then enrich and evaluate it against your controls.
No. Fianu observes the tools your teams already use and enforces policy in the pipeline. There are no new workflows to learn and nothing to add to a developer's day.
In your VPC. Fianu deploys into your own cloud so evidence and source data never leave your environment, which keeps security and compliance teams comfortable.
Controls and policies are fully configurable, so Fianu maps to whatever framework you're held to, SOC 2, ISO 27001, FedRAMP, FDA, PCI, or an internal standard.
Each attestation is cryptographically signed and tamper-evident, sealing the control result, the evidence behind it, and the policy it was judged against together.
Because Fianu plugs into your existing toolchain, most teams are generating signed attestations within days, not the months a governance program usually implies.


